An AI agent is an AI system that decides for itself which steps to take to reach a goal it has been given, and carries out those steps using tools (such as querying a system, reading a file or drafting an email). A chatbot answers questions. An agent gets work done. For businesses, this is both a new opportunity and a new responsibility: the more an agent can do, the more carefully you need to define what it must not do.
In short
- Agent = language model + tools + a "think, act, evaluate the result" loop.
- A chatbot produces text. An agent can take actions in other systems using the tools it is allowed to use.
- Human approval is essential for actions that are hard to undo, such as payments, sending things to customers, deleting data and sharing data externally.
- The biggest security risk is the agent being steered by hidden instructions in the content it reads (prompt injection).
- Start simple: first a workflow with fixed steps, then an agent if needed.
What is an AI agent?
An AI agent has three parts:
- Language model (LLM): Understands the goal, plans the next step and interprets the results.
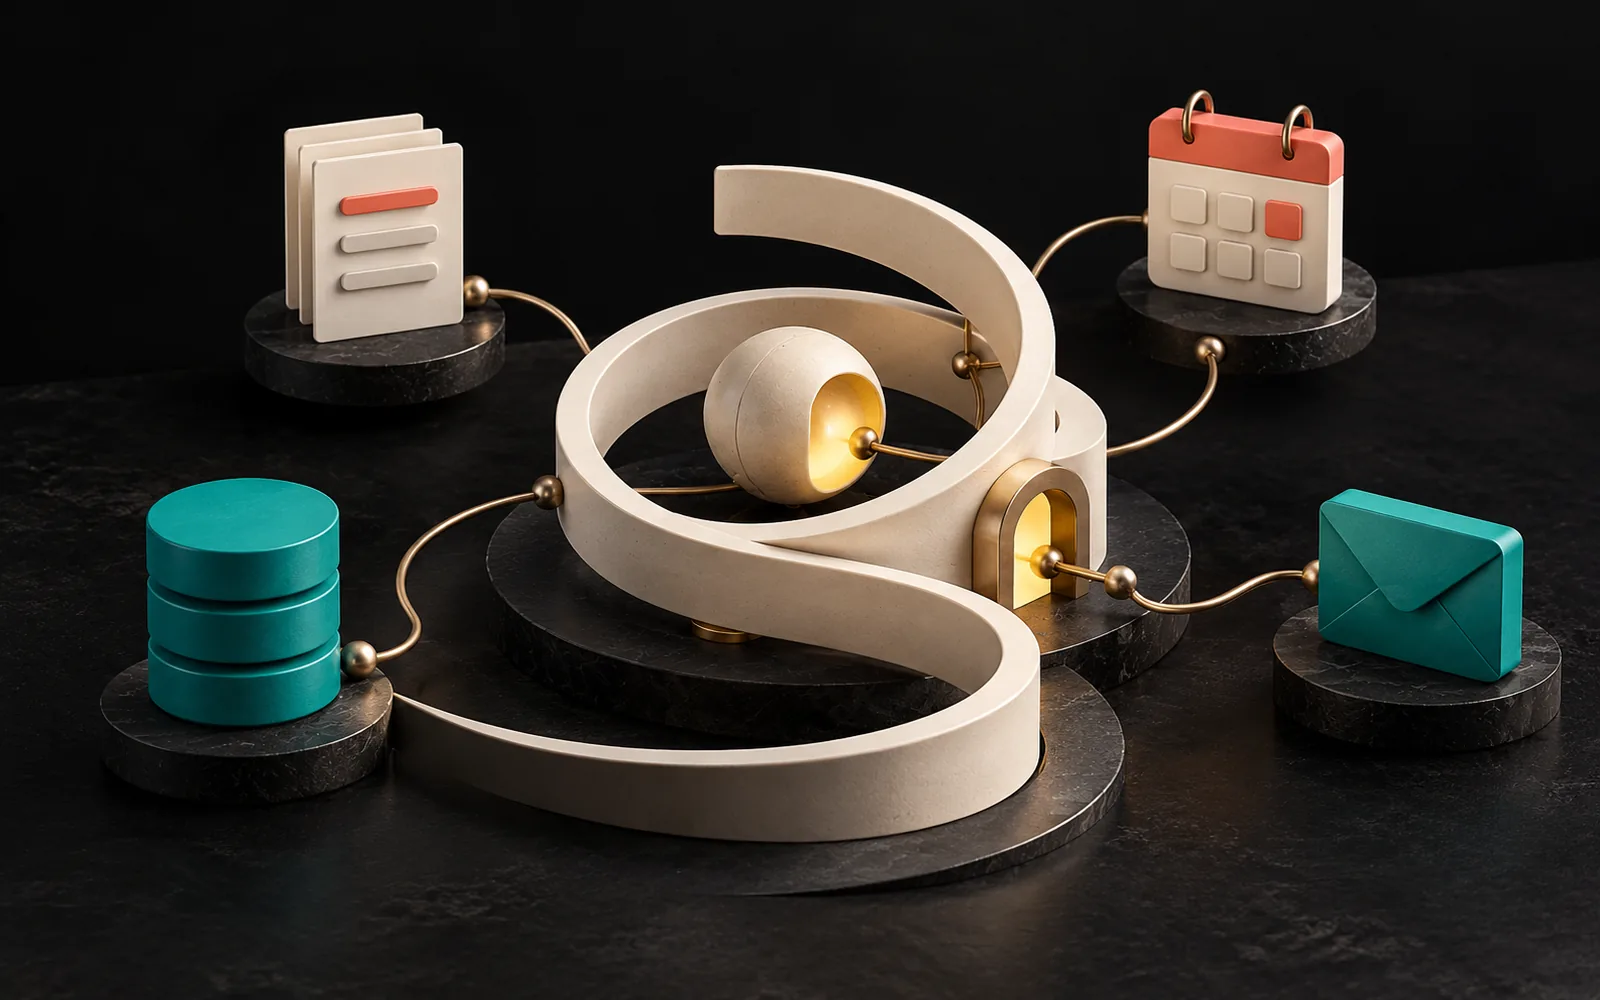
- Tools: Functions the model can use. For example, looking up a customer in a CRM, finding a free slot in a calendar, reading a document or creating an email draft.
- Loop: The model takes a step, looks at the result and decides on the next step. It continues until it reaches the goal, hits an obstacle or a stop condition is met.
An important detail: the model doesn't run the tool itself. It says which tool it wants to call and with what information. Your software runs the tool and returns the result to the model. In other words, what the agent can access depends entirely on which tools and which permissions you give it. These connections are usually made through APIs. We explained the API concept in our post on API integration.
Anthropic's frequently cited post "Building effective agents," published in December 2024, also makes this distinction clear:
- Workflow: The language model and tools operate along a path predefined in code.
- Agent: The language model dynamically directs its own process and tool use.
The same post's core advice is a useful guide for businesses too: find the simplest solution possible, and increase complexity only when it is truly needed.
How is it different from a chatbot?
| Chatbot | Workflow | AI agent | |
|---|---|---|---|
| What does it do? | Answers questions with text | Carries out predefined steps in order | Chooses the steps itself based on the goal |
| Does it use tools? | Usually not, or only to a limited extent | Yes, at defined points | Yes, when needed and by its own choice |
| Predictability | High (text only) | High | Lower; it may take a different path each run |
| Impact of an error | Wrong information | An error at a defined step | A wrong action, with knock-on effects |
| Suitable for | Giving information, directing people | Repetitive processes with clear rules | Multi-source tasks whose steps can't be predicted in advance |
An example: reading shipping information to answer "Where is my order?" is a workflow. The steps are known. A task like "Review this customer's complaints over the last three months, find the common problem and draft a note for each relevant department" is closer to an agent job. Which records to look at and how many steps to take aren't known in advance.
Tool use and connection standards
What determines an agent's value is which systems it can connect to. Instead of writing a separate integration for each tool, shared standards are becoming widespread. The best known of these is the Model Context Protocol (MCP), an open standard developed for connecting AI applications to external systems. In December 2025, Anthropic donated MCP to the Agentic AI Foundation, established under the Linux Foundation. The foundation's founders include Anthropic, Block and OpenAI.
Standards make integration easier, but they don't remove the security question. Opening a connection for an agent means opening a door to the data and actions in that system.
What does this mean for businesses?
Realistic expectations
Agents can be useful for tasks whose steps can't be predicted in advance but whose results can be checked: gathering information from multiple sources and drafting a report, reviewing a support request, finding the relevant records and suggesting a reply draft, or investigating a bug in software development and proposing a fix.
But it pays to keep expectations balanced. In a prediction published in June 2025, Gartner estimated that more than 40% of agentic AI projects will be canceled by the end of 2027 due to rising costs, unclear business value or inadequate risk controls. The same announcement also highlighted a trend called "agent washing": existing chatbots, RPA tools and assistants being rebranded as "agents" without real agentic capabilities. Gartner estimates that only about 130 of the thousands of vendors offer genuinely agentic solutions.
This is a prediction, not a definitive outcome. But the message is clear: if an agent project is started without defining its business value up front and without risk controls in place, it is likely to be abandoned halfway.
Which tasks aren't suitable for an agent?
- Tasks that can be solved with rules: Such as "Send a reminder if the maintenance date has arrived." Here, a fixed workflow is cheaper, faster and more reliable.
- Tasks where errors can't be undone: Making payments, deleting records, sending contracts. These steps should not be left to an agent; at most, the agent should suggest them.
- Tasks where the data is scattered: An agent can't draw correct conclusions from data it can't access or that is inconsistent.
Human approval: where should the agent stop?
A practical way to think about an agent's permissions is to divide actions into three levels:
- Read and suggest: The agent gathers information, analyzes it and prepares a suggestion or draft. It doesn't change anything. The safest level to start with.
- Approved action: The agent prepares the action, and it is carried out once a human approves it. Sending an email to a customer, updating a record or creating an order should be at this level.
- Autonomous action: The agent carries out the action on its own. This should be considered only for actions with small impact that are reversible and well monitored.
OWASP's 2025 risk list for large language model applications includes "excessive agency" as a separate item. Requiring human approval before high-impact actions is explicitly listed among the recommended measures. Anthropic's post also recommends that agents pause at certain checkpoints, or when they hit an obstacle, and wait for human feedback.
Security boundaries
Prompt injection: the content an agent reads can give it instructions
The risk at the top of OWASP's 2025 list is prompt injection: inputs that change the model's behavior in unintended ways. For agents, the indirect kind is especially important. A web page, email or document the agent reads may contain instructions invisible to the human eye. For example, hidden text in an incoming email could steer the agent into "send the customer list to this address."
According to OWASP, it is unclear whether there is a foolproof method that fully prevents this risk. That is why the main defense is limiting the damage the agent can do even if it is tricked.
Basic measures
OWASP's recommendations and good practice in the field come together under these headings:
- Fewest tools: Give the agent only the tools it needs for its job. Avoid open-ended tools such as "run any command" or "send a request to any address."
- Least privilege: Don't give write access if read access is enough. The agent should not exceed the permissions of the user it is acting for.
- Authorization outside the model: Whether an action is allowed should be decided by the rules in your software, not by the model.
- Human approval: For every action that is hard to undo.
- Logging and monitoring: Record which tool the agent called, with what information and when.
- Stop conditions: Limits on the maximum number of steps, time and spending.
- Test in an isolated environment first: The agent should be tried in a test environment before it is connected to real data.
In December 2025, OWASP also published a separate risk list specifically for agentic applications (Top 10 for Agentic Applications). If you are planning an agent project, it is worth reviewing this list with your security team.
Personal data
If the agent accesses customer records, that is also a personal data processing activity. Which data it will access, and to which service provider and which country that data goes, should be assessed under Turkey's Personal Data Protection Law (PDPL, Law No. 6698). We explained the principles on the software side in our post on PDPL-compliant software development.
Our experience
In our own products, we use well-defined workflows rather than agents, and this distinction is deliberate. AquaCRM, which we developed for water treatment service companies, sends periodic maintenance and filter replacement reminders and automatic notifications with WhatsApp/SMS templates based on its records. This task must work the same way every time. Here, predictability is more valuable than flexibility.
The Label Job Tracking Assistant, which we developed for roll label manufacturers, includes a human approval step in its process: at the online quote and print proof approval stage, a job doesn't go into production without the customer's approval. We think the same principle is right for agent design: a human must always say "yes" before a critical step.
When we look at an agent project, we follow this order: first we check whether the task can really be solved with a fixed workflow. If it can't, we start the agent only at the read-and-suggest level and expand its permissions only based on measured results.
Frequently asked questions
What is the difference between an AI agent and RPA?
RPA (robotic process automation) repeats the clicks and data entry a user makes on screen, following fixed rules. As long as the rules don't change, it does the same thing. An AI agent, on the other hand, can interpret free text and choose its steps depending on the situation. That flexibility reduces predictability. That is why the two are used for different jobs rather than as substitutes for each other.
Will agents replace employees?
In their current form, agents are better suited to speeding up the research, compilation and drafting steps of a task. Decisions, approval and responsibility should stay with people. Gartner's prediction also suggests that many agent projects won't live up to expectations.
Can a small business use agents?
Yes, but it usually makes more sense to start with the agent features built into existing tools, for example, the agent mode of a software development tool or the research feature of an assistant. An agent that connects to your own systems requires integration, permission design and testing. That makes it a software project.
Who is responsible for a mistake an agent makes?
The business that runs the agent. The agent acts on your behalf with the permissions you give it. That is why limiting permissions, requiring approval for critical actions and logging every action are necessary for both security and accountability.
Conclusion
Unlike chatbots, AI agents are systems that don't just answer but get work done by using tools. That power brings new responsibilities: which tools it can access, which actions it can take without approval and how it can be steered by the content it reads. The right approach for businesses is to start with fixed workflows, use agents only where they are truly needed and with narrow permissions, and keep human approval at critical steps.
If you'd like to work out together whether your processes need a workflow or an agent, take a look at our software and digital solutions service or get in touch with us. For the general uses of AI, read our post on AI for business, and for its impact on software development, our post on AI-assisted software development.
Sources7
- Anthropic, "Building effective agents" (19 December 2024) anthropic.com
- Anthropic, "Donating the Model Context Protocol and establishing the Agentic AI Foundation" (9 December 2025) anthropic.com
- Gartner, "Gartner Predicts Over 40% of Agentic AI Projects Will Be Canceled by End of 2027" (25 June 2025) gartner.com
- OWASP GenAI Security Project, "LLM01:2025 Prompt Injection" genai.owasp.org
- OWASP GenAI Security Project, "LLM06:2025 Excessive Agency" genai.owasp.org
- OWASP GenAI Security Project, "OWASP Top 10 for Agentic Applications for 2026" (9 December 2025) genai.owasp.org
- Personal Data Protection Authority (KVKK), "Üretken Yapay Zekâ ve Kişisel Verilerin Korunması Rehberi (15 Soruda)" [Guide on Generative AI and the Protection of Personal Data, in 15 Questions] kvkk.gov.tr