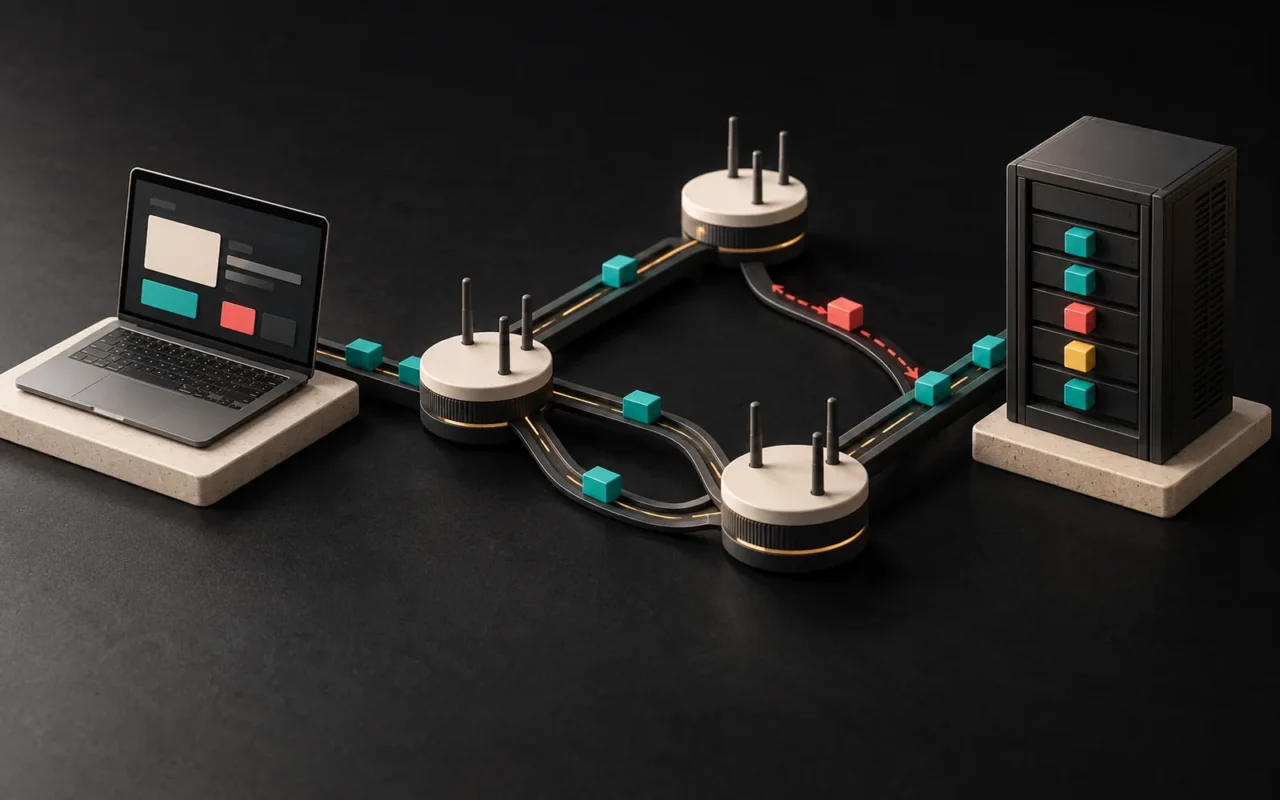
HTTP vs HTTPS: the difference comes down to one letter, and the "S" stands for secure. HTTP is the set of communication rules your browser and a server use to exchange pages, images and form data. HTTPS, on the other hand, is the same communication, encrypted with TLS and with the server's identity verified. With HTTP, someone in the middle can read and change the traffic; with HTTPS, they can't.
In short
- HTTP (HyperText Transfer Protocol) is the web's request-response protocol. It uses port 80 by default.
- HTTPS is HTTP encrypted with TLS. It uses port 443 by default.
- HTTPS provides three things: confidentiality (encryption), integrity (data isn't changed in transit) and authentication (you are connected to the right server).
- Since July 2018, Chrome has marked HTTP pages as "Not secure."
- The most common problems when switching to HTTPS: missing redirects, mixed content and old links.
What is HTTP?
HTTP is the protocol that sets the rules for how your browser asks a server for something and gets an answer. When you open a page, the browser tells the server "give me this page" (the request), and the server returns the page along with a status code (the response). Some status codes you often see:
- 200 OK: The request succeeded.
- 301 Moved Permanently: The page has permanently moved to another address.
- 404 Not Found: The page couldn't be found.
- 500 Internal Server Error: An error occurred on the server.
HTTP is a stateless protocol: each request is independent of the one before it. So when websites "remember" you (keeping you logged in, holding on to your cart), extra mechanisms such as cookies handle that.
However, HTTP on its own includes no encryption. As a result, everything you send travels across the network as plain text.
What is HTTPS?
HTTPS is the HTTP conversation carried out inside a security layer called TLS (Transport Layer Security). The protocol itself, meaning the requests, responses and status codes, stays the same; what changes is that the conversation happens inside a tunnel.
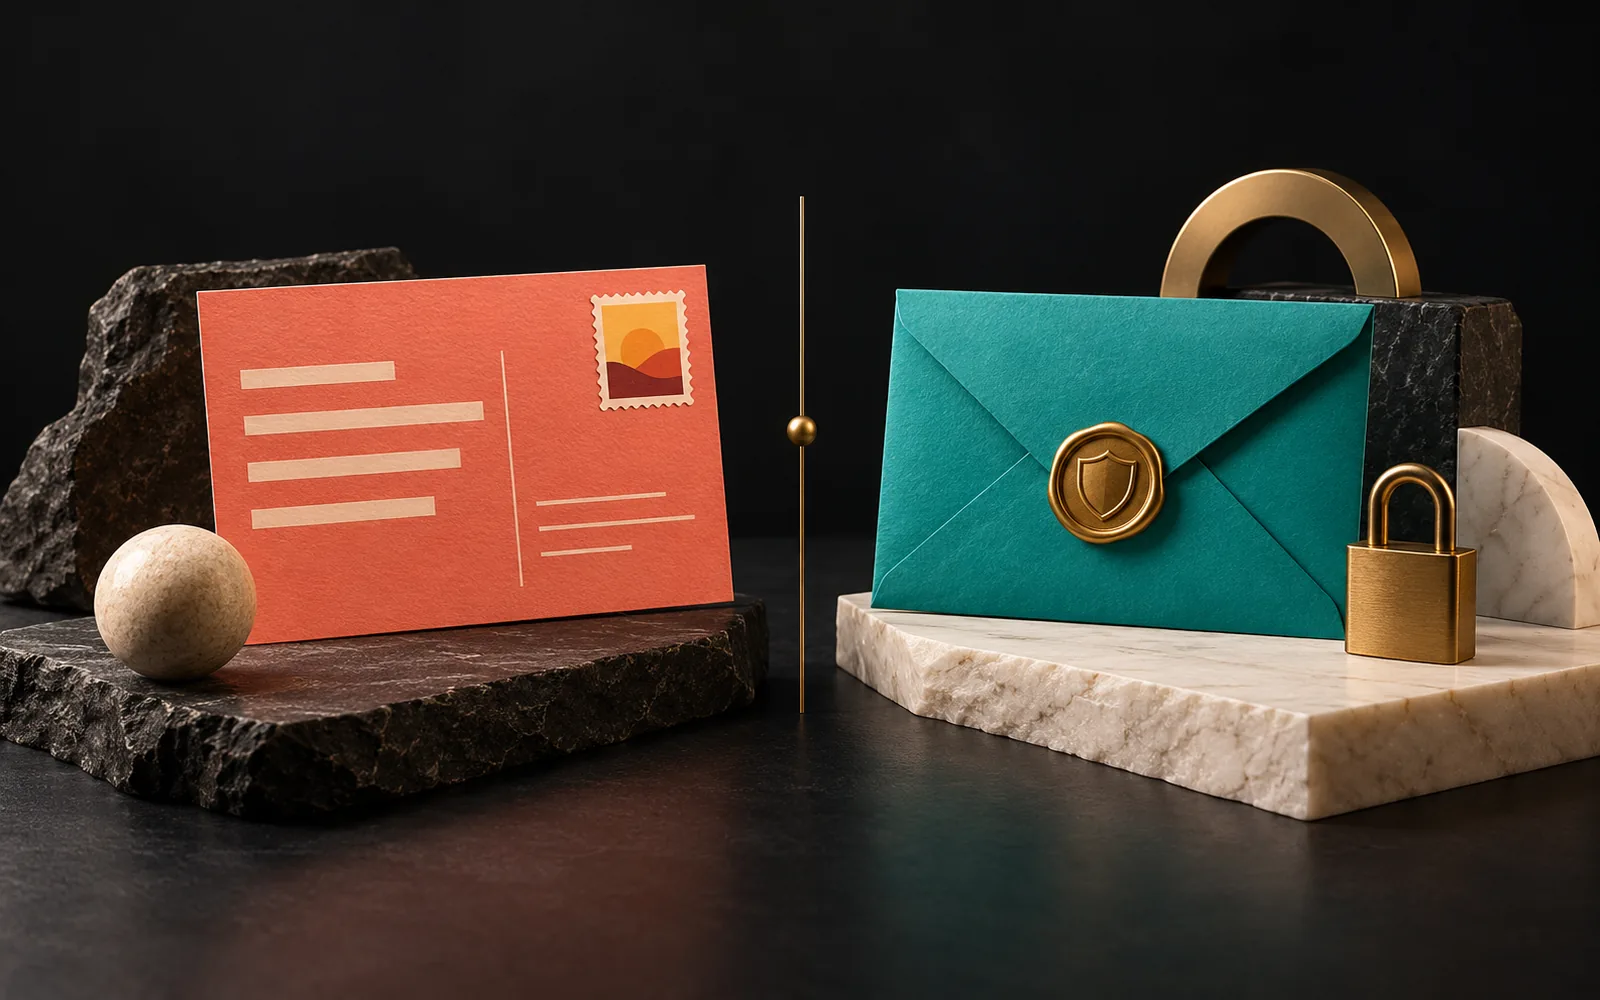
An analogy: sending data over HTTP is like mailing a postcard. The mail carrier and anyone else along the way can read what you wrote. HTTPS, by contrast, is like a sealed envelope that only the right recipient can open.
Here is roughly what happens when an HTTPS connection is set up:
- The browser connects to the server and says it wants a secure connection.
- The server sends the SSL/TLS certificate for the domain.
- The browser checks that a trusted authority signed the certificate, that it hasn't expired and that it matches the domain being visited.
- The two sides agree on session keys that only they know.
- From then on, these keys encrypt all HTTP traffic.
We covered what a certificate is, the types and where to get one in detail in our article What is an SSL certificate?. This article, instead, focuses on the difference between the protocols and how it affects your website.
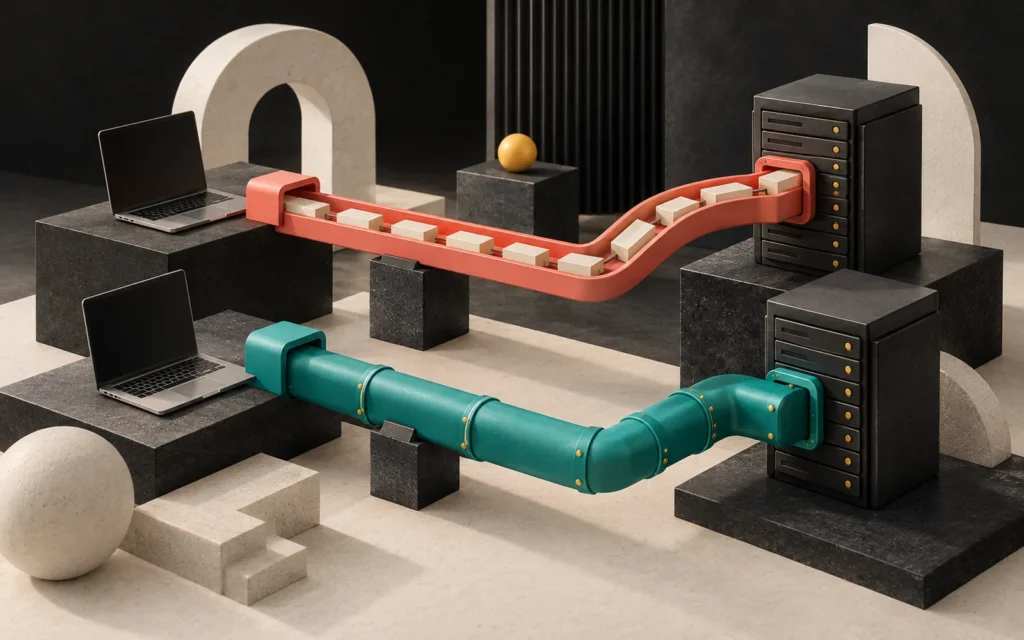
HTTP vs HTTPS compared
| Feature | HTTP | HTTPS |
|---|---|---|
| Address prefix | http:// | https:// |
| Default port | 80 | 443 |
| Encryption | None | Yes, with TLS |
| Server authentication | None | Yes, with a certificate |
| Protection against data being changed in transit | None | Yes |
| What the browser shows | "Not secure" warning | No warning |
| HTTP/2 and HTTP/3 support (in browsers) | Not in practice | Yes |
| Browser features such as location, notifications and camera | Not available | Available |
How HTTPS affects your website and your business
Visitor trust
Since version 68, released on 24 July 2018, Chrome has shown every HTTP page as "Not secure" in the address bar. On a page with a quote request or contact form, this warning can directly affect whether a visitor leaves their details.
One detail: with version 117, released in September 2023, Chrome also removed the padlock icon from the address bar and replaced it with a neutral "settings" icon. Google's reasoning was that HTTPS is now the default, and many users misread the padlock as meaning "this site is trustworthy." In other words, HTTPS is no longer a mark of distinction but the minimum that people expect.
Data security
For example, on public Wi-Fi networks, someone on the same network can read form data sent over HTTP. It is also possible to intercept an HTTP page and inject ads or malicious code. HTTPS removes both risks.
Search engines
In August 2014, Google announced that it had started using HTTPS as a ranking signal and described it as a "very lightweight" signal. Therefore, HTTPS alone won't lift you to the top; Google weighs it together with other factors such as content and user experience.
Speed
The idea that HTTPS slows a website down is largely a thing of the past. On the contrary, browsers in practice only use the modern, faster protocols HTTP/2 and HTTP/3 over encrypted connections. So switching to HTTPS also opens the door to speed improvements.
Browser features
In addition, many browser features, including location data, push notifications (Web Push), camera and microphone access and service workers, only work over secure connections. If you want to add a feature like this to your website later, HTTPS is a prerequisite.
Common mistakes when switching to HTTPS
- Leaving the HTTP version open. Once you install the certificate, every request that arrives via
http://should be sent to thehttps://address with a permanent (301) redirect. Otherwise, two copies of the website stay accessible. - Mixed content. This means images, scripts or stylesheets loaded over
http://inside an HTTPS page. Modern browsers try to upgrade images to HTTPS automatically, but they block scripts and stylesheets. The result: pages that look broken, menus or forms that don't work. - Old addresses in the database. In systems like WordPress, the site address, image links in content and theme settings can remain as
http://in the database. You need to update these during the switch as well. - Forgetting external services. Also update your site address in Search Console, analytics tools, ad accounts and social media profiles.
- Inconsistent
wwwand non-wwwaddresses. Whichever address you chose as your main address, the other three combinations (http/https×www/non-www) should redirect to it.
HSTS: one step further
HSTS (HTTP Strict Transport Security) is a header that lets the server tell the browser "from now on, connect to this site only over HTTPS." After that, it converts the request straight to HTTPS even if the user types http://. You should only turn on HSTS after making sure all of the site's subdomains are ready for HTTPS; otherwise, a subdomain without HTTPS may become unreachable.
Our experience
Most of the websites we build run on WordPress, and when we take them live we switch to HTTPS using a checklist: the certificate covers both the main domain and the www version, every address combination redirects to a single main HTTPS address with a 301, old http:// links in the database are updated, and no mixed content warnings remain in the browser console. We explained the certificate itself and its renewal in our SSL certificate article, and how a domain connects to a server in What is DNS?.
Frequently asked questions
Is every website with HTTPS trustworthy?
No. HTTPS only verifies that the connection is encrypted and that the website belongs to that domain. However, it doesn't show that the site's owner is honest. Fraudulent websites can use HTTPS too, so you still need to check the domain carefully.
Does a simple brochure website without a form need HTTPS too?
Yes. Browsers mark every HTTP page as "Not secure," whether or not it has a form. HTTPS also prevents the page from being changed in transit and makes it possible to use faster protocols.
Will my search rankings drop when I switch to HTTPS?
If you do the switch correctly, you shouldn't expect a lasting loss. What matters is that you redirect all old addresses to the new ones with a 301, update the sitemap and add the HTTPS version in Search Console.
Will HTTPS slow down my website?
With today's hardware and protocols, the extra load from encryption is very small. In fact, HTTPS is a prerequisite for using faster protocols such as HTTP/2 and HTTP/3.
Conclusion
The difference between HTTP and HTTPS is whether your data travels on an open postcard or in a sealed envelope. Today, HTTPS is the minimum standard for every business website. When you switch, checking redirects, mixed content and old links ensures that both users and search engines see your website without problems. In our web design and WordPress development projects, setting up HTTPS is a standard step in the launch process. If you see a "Not secure" warning on your current website, get in touch.
Learn more on Grafik Sanat (in Turkish): Visual explanations and quizzes on this topic → grafiksanat.com.tr/terim/http-https
Chrome's plan to make HTTPS the default
Update (October 2026): In October 2025, Google announced its plan to make HTTPS the default in Chrome. Under this plan, the public-sites version of the "Always use secure connections" setting will be turned on by default for Enhanced Safe Browsing users in April 2026 (Chrome 147), and for all users with Chrome 154, scheduled for release in October 2026. With this setting on, Chrome will ask the user for permission before visiting a public website without HTTPS for the first time. For websites that remain on HTTP, this means visitors will see a warning screen before they reach the site.
Sources11
- IETF RFC 9110 — HTTP Semantics (stateless protocol; port 80 for http, port 443 for https; server authentication) — accessed: 2026-10 rfc-editor.org
- PKI Consortium — Chrome will show "Not secure" for all HTTP sites starting July 2018 (Chrome 68) — accessed: 2026-10 · Chrome Releases — Stable Channel Update for Desktop (24 July 2018) — accessed: 2026-10 pkic.org
- Chromium Blog — An Update on the Lock Icon (2 May 2023) — accessed: 2026-10 blog.chromium.org
- Help Net Security — Google Chrome will lose the "lock" icon for HTTPS-secured sites (3 May 2023; Chrome 117) — accessed: 2026-10 helpnetsecurity.com
- Google Search Central Blog — HTTPS as a ranking signal (August 2014) — accessed: 2026-10 developers.google.com
- MDN — Mixed content — accessed: 2026-10 developer.mozilla.org
- MDN — Strict-Transport-Security — accessed: 2026-10 developer.mozilla.org
- MDN — Features restricted to secure contexts — accessed: 2026-10 developer.mozilla.org
- Apache httpd — mod_http2 README (browsers support HTTP/2 only over TLS) — accessed: 2026-10 apache.googlesource.com
- IETF RFC 9114 — HTTP/3 (runs over QUIC; QUIC includes TLS 1.3) — accessed: 2026-10 rfc-editor.org
- Google — HTTPS by default (Chrome Security, 28 October 2025) — accessed: 2026-10 blog.google