DNS (Domain Name System) is the system that translates a domain name such as example.com.tr into the IP address of the server where your website lives. When a visitor types your address, the browser first asks DNS, "Which address is this name at?" and connects to the server once it gets the answer. Whether your site loads and whether your email reaches the right place both depend on your DNS records being correct.
In short
- DNS is a directory system, distributed around the world, that translates domain names into IP addresses.
- Your domain's DNS records are kept on the nameservers you specify at your registrar.
- The A record points to your website, the MX record handles email, and TXT records hold verification and email security settings.
- TTL sets how long a record is kept in cache. That is why DNS changes seem to "propagate slowly."
- A small DNS mistake can take down your website or your business email.
What is DNS?
Every server on the internet has a numeric address: its IP address. People, on the other hand, remember names. DNS translates between the two. In the common analogy, it is the phone book of the internet.
DNS is not a single list stored on one server. It is a hierarchical, distributed system shaped like a tree. At the top are the root servers. The root server system consists of 13 root server identities (A through M), operated by 12 independent organizations. Each identity has many copies spread around the world. Below the root are the servers for extensions such as .com and .tr, and below those are the servers that hold the records for individual domain names.
How does DNS work? The journey of a query
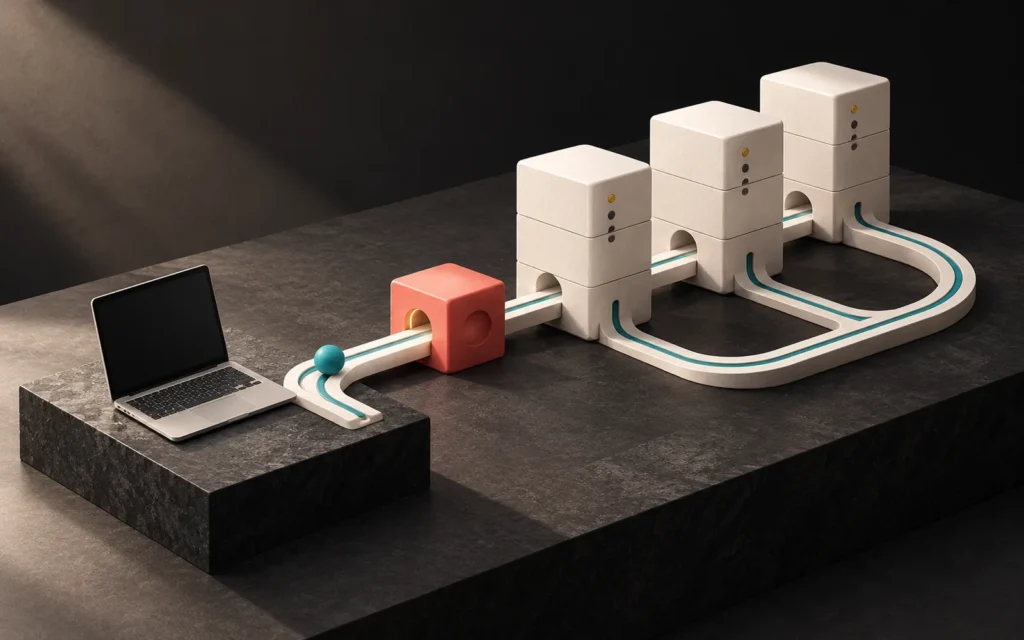
When a visitor types example.com.tr into the browser, these steps happen in the background:
- Cache check: The browser and the operating system check whether they have looked up this name recently. If the answer is in the cache, the process ends here.
- Question to the resolver: If not, the question goes to a recursive resolver, usually run by your internet service provider or by a DNS service you have chosen.
- Search from the root: If the resolver doesn't know the answer, it is referred to the root servers, then to the
.trservers, and from there to your domain's authoritative nameserver. - Answer: The authoritative nameserver returns the domain's IP address. The resolver stores this answer for the length of the TTL and passes it to the browser.
- Connection: Now that the browser knows the IP address, it connects to the server and requests the page.
This journey usually takes the blink of an eye. By standard, DNS queries run over port 53.
DNS records you should know as a business owner
When you open your domain's DNS settings, you see a table. Each row is a record. The ones you will run into most often:
| Record | What it does | Example use |
|---|---|---|
| A | Points the domain to an IPv4 address | Which server is your site on? |
| AAAA | Points the domain to an IPv6 address | If your server supports IPv6 |
| CNAME | Points one name to another name (an alias) | Pointing www to the main domain |
| MX | Says which server email should be delivered to | Your business email service |
| TXT | Free text, used for verification and security | Google Search Console verification, SPF |
| NS | Shows which nameservers manage the domain | Your hosting or DNS provider |
Most of these records are part of the core definition of DNS, the RFC 1034 and RFC 1035 standards from 1987. The AAAA record used for IPv6 was added later.
Where do you set the nameservers?
At the registrar where you bought your domain, you specify which nameservers your domain should use. For example, your hosting company gives you two addresses such as ns1.hostingcompany.com and ns2.hostingcompany.com. From then on, you manage your DNS records in that company's control panel. Knowing which panel to edit solves many "I changed it but nothing happened" problems.
TTL: why does "DNS propagation" take time?
Every DNS record has a TTL (Time To Live) value. It is measured in seconds and tells resolvers, "Keep this answer for no longer than this." If the TTL is 3600, the record stays in cache for one hour.
That is why, when you change a record, not every resolver in the world sees the new value at the same time. A resolver holding the old answer in its cache keeps returning the old address until the TTL runs out. People call this "DNS propagation." In reality nothing is spreading; caches are simply expiring.
Practical tip: A day before a planned change such as a server migration, lower the TTL of the relevant record (for example, to 300 seconds). After the change, once everything works, raise the TTL again. This shortens the transition.
How does DNS affect your website and your business?
- Availability: If DNS doesn't respond, your site won't load even if your server is running. That is why the reliability of your nameserver service matters.
- Email: If the MX record is wrong or deleted, incoming email won't reach you. If TXT records such as SPF are missing, the email you send may land in the recipient's spam folder.
- Speed: Each new visitor triggers a DNS lookup. A DNS provider with fast, widespread infrastructure shortens the first connection.
- Security: When attackers use fake DNS answers to send users to the wrong site, it is called DNS poisoning (spoofing). DNSSEC is an extension that verifies DNS answers really come from the authoritative source and haven't been altered. Note: DNSSEC does not encrypt data; it only proves that the data is authentic.
Common DNS mistakes
- Changing nameservers without moving the old records. Setting up only the A record at a new provider and forgetting the MX and TXT records is one of the best-known reasons email stops working.
- Editing in the wrong panel. If your domain is registered with one company and your nameservers are at another, the records are managed in the second company's panel.
- Forgetting the
wwwrecord.example.com.trloads, butwww.example.com.trdoesn't. - Conflicting records for the same name. A name cannot have a CNAME and other records at the same time; this leads to unexpected behavior.
- Losing access to the DNS panel. If only your former agency knows the panel login, even the simplest change can take days.
Our experience
In website projects, we make a copy of the domain's existing DNS records before going live. That way the email (MX) and verification (TXT) records aren't lost when the nameservers change. For server changes, we lower the TTL in advance and plan the switchover, and we make sure access to the DNS panel stays with our client. We cover ownership and renewal of the domain itself in detail in our post What is a domain name?.
Frequently asked questions
How long does a DNS change take to work?
It depends on the TTL of the record. Resolvers may keep the old answer for the length of the TTL. If the TTL is one hour, most users will see the change within an hour at most. Nameserver changes can take longer, because the records on the higher-level servers also have to expire.
Can I get my domain and my hosting from different companies?
Yes. You either point your domain's nameservers to your hosting company, or you keep your nameservers and just set the A record to the hosting server's IP address. Both are common approaches.
My site loads but my email isn't arriving. Could it be DNS?
Very likely, yes. Check whether the MX record points to the correct mail server. If the problem started after a nameserver change, the MX record is the first place to look.
Is a free DNS service enough?
For most of a business website's needs, the DNS service offered by your hosting or domain company is enough. What matters is that it is reliable, that you have access to the panel and that the records are kept in order.
Conclusion
Visitors never see DNS, yet your website and your email depend on it. Knowing which panel manages it, keeping a copy of your records and making changes with the TTL in mind prevents most problems. In our web design and WordPress development projects, we treat domain and DNS settings as part of the launch plan. If you are planning a new site, we also recommend reading what to check before commissioning a corporate website.
Learn more on Grafik Sanat (in Turkish): Visual explanations and quizzes on this topic → grafiksanat.com.tr/terim/dns
Sources5
- IETF RFC 1034 — Domain Names: Concepts and Facilities (hierarchy, resolvers, TTL, delegation) — accessed: 2026-10 rfc-editor.org
- IETF RFC 1035 — Domain Names: Implementation and Specification (port 53, A/NS/CNAME/MX/TXT records) — accessed: 2026-10 rfc-editor.org
- IETF RFC 3596 — DNS Extensions to Support IP Version 6 (AAAA record) — accessed: 2026-10 rfc-editor.org
- IETF RFC 4033 — DNS Security Introduction and Requirements (DNSSEC; does not provide confidentiality) — accessed: 2026-10 rfc-editor.org
- Root Server Technical Operations — root-servers.org (13 identities, 12 operators) — accessed: 2026-10 root-servers.org